 Skip to content

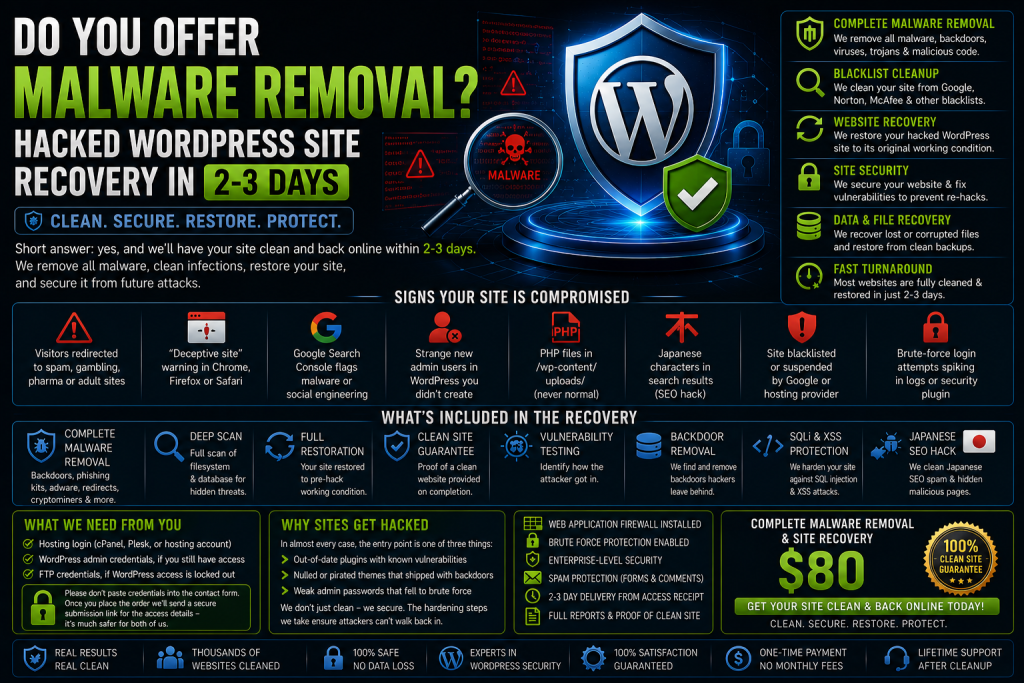
Short answer: yes, and we’ll have your site clean and back online within 2–3 days. Hacked WordPress sites are something we deal with regularly — sometimes for our own hosting clients, sometimes for one-off jobs sent in via the contact form. If you’ve just discovered your site is infected, redirecting to spam, blacklisted, or simply behaving strangely, this is the service you need.
Signs Your Site Is Compromised
- Visitors report being redirected to gambling, pharma or adult sites they didn’t click on
- Chrome, Firefox or Safari is showing a “deceptive site ahead” warning — we cover the recovery path for that specifically in why Chrome says your site is dangerous and how to fix it
- Google Search Console has flagged the site for malware or social engineering
- Strange new admin users appeared in WordPress that you didn’t create
- Files in
/wp-content/uploads/that look like PHP scripts (uploads should never contain executable PHP) - Japanese characters appearing in your search results — the “Japanese SEO hack”
- The site is in Google’s blacklist or your hosting provider has suspended it for malware
- Brute-force login attempts spiking in your logs or security plugin
If any of the above is happening, time matters. Every hour the malware stays live is more reputational damage, more lost rankings, and a higher chance of Google’s abuse report systems escalating to a hard takedown.
What’s Included in the Recovery
- Complete malware removal — backdoors, phishing kits, adware injections, redirect scripts, cryptominers, the lot
- Deep malware scan across the full filesystem and database
- Full restoration of site health — your site working as it did pre-hack
- Guarantee and proof of a clean website on completion
- Blacklist removal if your domain has been listed (Google Safe Browsing, Norton, McAfee, etc.)
- Vulnerability testing to identify how the attacker got in
- Backdoor removal — most hackers leave a way back in; we find and close them
- SQL injection and XSS prevention hardening
- Malicious redirect code removal
- Japanese SEO hack removal if applicable
- Web application firewall installed and configured
- Brute force protection — login attempt limits, admin URL hiding, file editing disabled
- Enterprise-level security configuration
- Spam protection on forms and comments
- 2-3 day delivery from receipt of access credentials
What We Need From You
- Hosting login (cPanel, Plesk, or hosting account)
- WordPress admin credentials, if you still have access
- FTP credentials, if WordPress access is locked out
Please don’t paste credentials into the contact form. Once you place the order we’ll send a secure submission link for the access details — it’s much safer for both of us.
Why Sites Get Hacked in the First Place
In almost every case we investigate, the entry point is one of three things: an out-of-date plugin with a known vulnerability, a nulled or pirated theme that shipped with a backdoor, or a weak admin password that fell to brute force. Hosting environments rarely get compromised at the server level — it’s almost always the application layer.
That’s why our malware removal isn’t just a clean-up — we close the door behind us. The hardening steps included above exist specifically so the next attacker doesn’t walk back in the same way the last one did. For a deeper read on the broader security picture, our piece on protecting your investment from hackers covers the strategic side.
Pricing
- ✅ Complete malware + backdoor removal
- ✅ Deep scan of files and database
- ✅ Full site restoration
- ✅ Blacklist removal (where applicable)
- ✅ Vulnerability testing + closure
- ✅ WAF + brute-force protection
- ✅ Japanese hack removal if needed
- ✅ 2-3 day delivery
- ✅ Guarantee + proof of clean site
How To Order
Submit the form below with your URL and a quick note on what’s going wrong. Or contact us directly on Telegram at @pbn_hosting_sl or by email at [email protected]. We respond fast on hacked-site jobs because we know every hour counts. Other service questions are answered over on the PBN hosting FAQs page.